Nine Things a Microsoft 365 Security Review Finds Almost Every Time
The same findings come up in nearly every tenant we assess. Nine of them, what each one actually costs you, and how to check your own as you read.
The same findings come up in nearly every tenant we assess. Nine of them, what each one actually costs you, and how to check your own as you read.
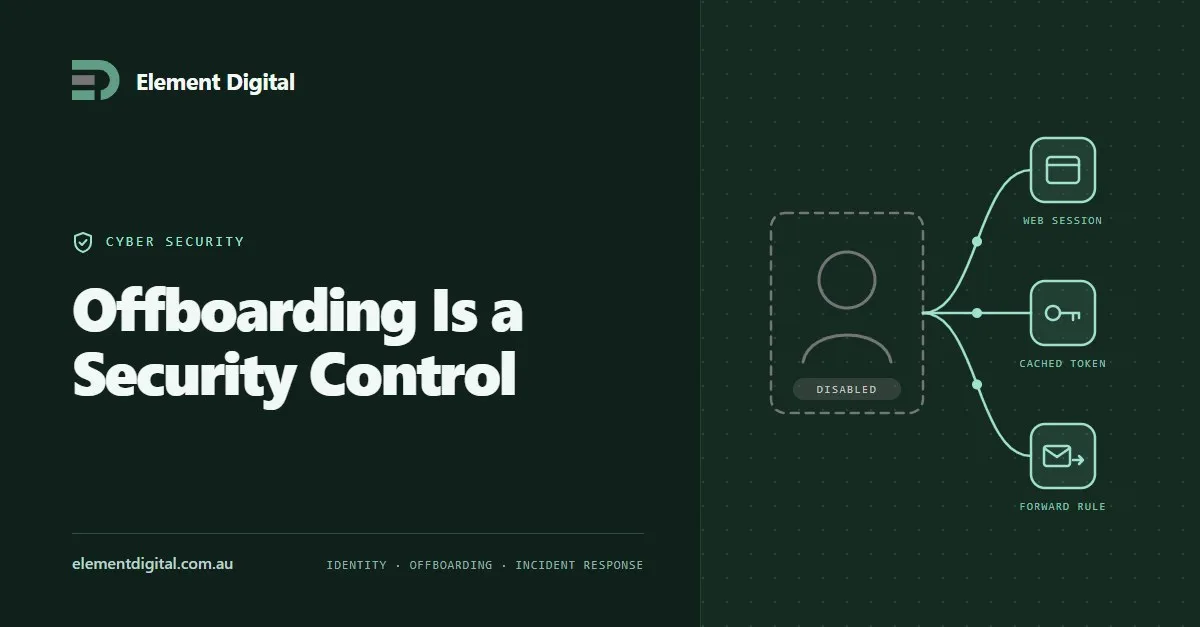
Removing someone’s account is not the same as removing their access. Where access survives, why it is hard to investigate later, and the sequence that works.
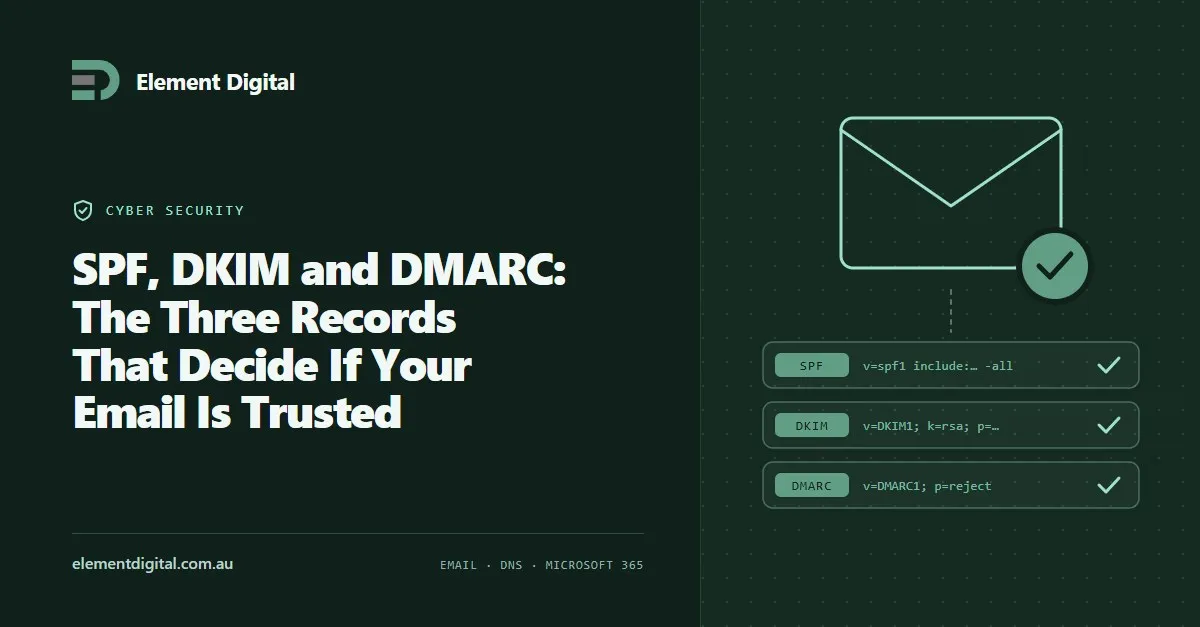
Three DNS records decide whether the world trusts mail from your domain. Most businesses have one of them and have never looked at the other two.
AppLocker, App Control for Business, ThreatLocker and Airlock Digital compared against the Essential Eight maturity levels, with indicative pricing, implementation effort and ongoing management.
Ingest, storage and features drive most of a SIEM bill. Log tiering is the lever most people miss, and it moves the number more than any discount will.
Passwords are being replaced by passkeys, and the technology is finally ready. What passwordless gives you, and what it takes to get there.
Frameworks, strategies, standards and regulations are different things. Where NIST CSF, the Essential Eight, CIS, PCI DSS, ISO 27001 and GDPR each sit.
What we learned hardening our own environment against the Essential Eight, including the parts that cost the most and the compliance tools that overpromise.
Three controls stop most attacks on a small business: multi-factor authentication, patching the right things first, and staff who know what to report.
A password safe is the cheapest security fix most small businesses can make. What one does, which to pick, and how to roll it out.
MFA stops most account takeovers, but not all MFA is equal. Why SMS codes are the weak option, and why passkeys are now the one to aim for.
In today’s digital age, technology has become an integral part of our lives.
Let us talk about what you are trying to achieve, no obligation, just a conversation.